Bob MartinezPerson
svc-backupService account
Find overlooked identities
Inspect human and service identities, credential age, and available activity evidence.
Who can reach what matters.
Theodolite surveys human and service identities across AWS, Azure, and SharePoint, brings their reported permissions together with sensitive-data evidence, and gives your team a prioritized fix list.
Service account · SharePoint
187 personal-data matches
An aging credential, an owner to identify, and personal-data indicators to investigate.
Provider-reported. Effective access shown when verified.
People leave. Service accounts stay. Permissions accumulate. Bring identities and resource permissions into the same view so your team can decide where to look first. Coverage follows the sources and permissions you authorize.
Inspect human and service identities, credential age, and available activity evidence.
SharePointFollow reported permissions to associated resources and examine the supporting source evidence.
See which access questions need an owner, a closer review, or more evidence.
See which sources were inspected and which need attention. Missing permissions and unsupported content appear alongside your results, with the scope and reason for each gap.
The denied scope stays uninspected. Evidence collected elsewhere remains available.
Review the affected scope and reason in the environment details. Confirm the intended scanner permissions with the environment owner.
A discovered file is not always analyzed content. When the scanner cannot process its format, the file remains listed with its inspection status.
Use the reason recorded for the affected file to decide what needs a different review method.
Uninspected content is not an all-clear.
Open a document to see detected patterns, match counts, and source context. Give your team the evidence to assess what deserves attention.
SharePoint / Engineering / Shared Documents
api_keyAPI-key patterns were detected in these deployment notes. Review the source and the credential-remediation guidance in Top priorities.
Automated matches need review before confirming a classification.
See the evidence and recommended remediation together.
SharePoint
Critical
3 matches
SharePoint
Critical
6 matches
Review findings and recommendations; they do not remediate your environment.
A typical year, a bad year, and a single incident answer different questions. Explore the modeled range and the chance of exceeding a loss threshold, including years with no incident. Theodolite and its report use the same three measures.
Annual P25–P75, including zero-incident years.
Annual P99. Not a maximum.
Individual-incident P25–P75.
37.09% modeled chance of annual losses exceeding $41,053.
Typical year includes all modeled years, including those with no incident. A $0 lower bound does not mean zero risk. Bad year (1-in-100) is an annual tail threshold, not a maximum or a fixed schedule; tied values can mean fewer than 1% of years exceed it. Per incident describes individual losses, not totals for years with incidents.
This illustration assumes an average of 0.5 incidents per year and an incident-loss distribution with a $250,000 median and a $2 million 95th percentile. These are scenario inputs, not customer observations or a forecast.
Illustrative results; customer estimates require evidence, approval, and completed validation.
Deploy in AWS or Azure. Connect the sources your administrator authorizes and keep detailed findings in your environment.
Review the resources and supported content your scanner is authorized to read.
Review initial evidence within a bounded processing window.
Continues automatically into a deeper review, with coverage gaps kept visible.

Reads the sources you authorize
In your scanner database
In your secret store
Requested details transit Theodolite over TLS.
Zero central persistenceReview findings, observed access, and priorities.
The connection starts outbound from your scanner; your browser reviews the requested results through the relay.
The scanner uses the permissions granted to its workload identity and supported connectors. Additional accounts or subscriptions require explicit grants and registration.
Survey scope follows permissions, supported content, and processing limits.
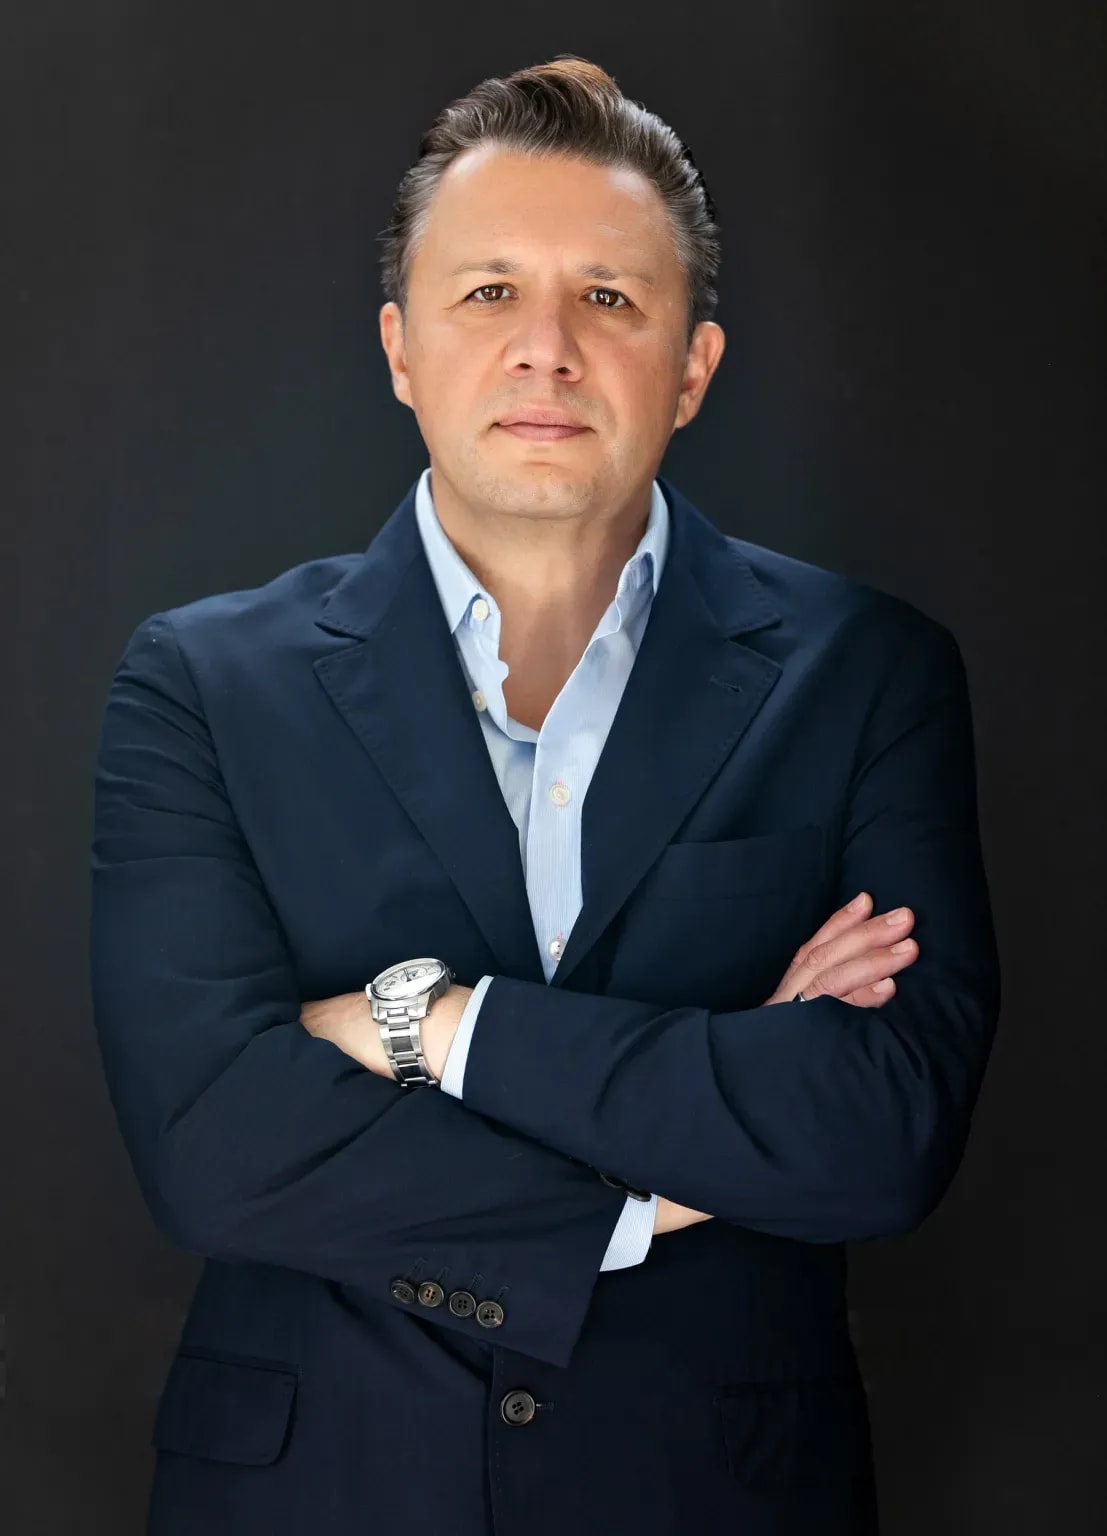
Use Theodolite as a standalone product. If your team wants help interpreting results or planning next steps, vCSO.ai advisory support is available separately.
Founder, vCSO.ai
Former Chief Security Officer
Silicon Valley Bank · 2007–2021
An evidence-led view of identities, resource permissions, sensitive-data indicators, and prioritized security findings. Explore the source behind a result, follow the recommended next steps, and see where coverage needs attention.
The report view can be printed or saved as a PDF when its required data is available.
Select “Request a sample survey” to discuss your sources and arrange assisted onboarding. Your administrator approves the scanner deployment, source permissions, and associated cloud costs before work begins.
A Sample survey gathers initial evidence within a bounded processing window, then continues automatically into a distinct Full survey. Volume, permissions, and provider response times affect completion.
The request itself needs no cloud access and starts no survey.
Detailed findings stay in your customer-hosted scanner database. Connector secrets stay in your customer-controlled secret store.
Requested details transit Theodolite encrypted and in memory for authorized viewing. Operational state and permitted run summaries may be retained centrally.
Supported scanning reads the sources you authorize. Installation creates the scanner’s own cloud resources; any permission to update that infrastructure is separate from access to your source data.
The loss engine is in validation, with an illustrative scenario on the homepage. Theodolite and its report use three measures: Typical year (annual P25–P75, including no-incident years), Bad year (1-in-100, annual P99), and Per incident (individual-incident P25–P75). Customer estimates require qualified evidence, an approved model, and completed validation; individual files, identities, and findings are not assigned dollar values.
Tell us which environments you want to review. We’ll discuss the scope, show you the product, and help your administrator prepare for the Sample survey.